Cyberattack Triggers False Nuclear Alerts Across Ukrainian and Russian Air Raid Networks
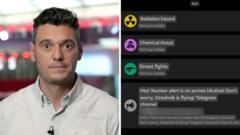
Official air alert applications in both Ukraine and Russia were compromised on Sunday evening, broadcasting erroneous nuclear hazard warnings to citizens. Cybersecurity experts and government officials have yet to identify the perpetrators behind the sophisticated digital breach.

- Simultaneous cyber intrusions compromised official air alert platforms in both Ukraine and Russia on Sunday evening.
- The breaches triggered false notifications warning populations of imminent nuclear threats, causing widespread confusion.
- Neither administration has officially attributed responsibility for the high-profile digital attacks as investigations get underway.
Official mobile alert platforms utilized by both Ukraine and Russia to warn citizens of incoming aerial strikes suffered simultaneous cyber intrusions on Sunday evening, resulting in the mass dissemination of fraudulent nuclear hazard warnings. The unauthorized broadcasts sparked momentary panic and widespread confusion among populations already living under the severe strain of ongoing wartime conditions.
This unprecedented simultaneous compromise highlights the extreme vulnerability of critical civilian warning infrastructure amid the ongoing geopolitical conflict. While both nations heavily rely on digital applications to deliver life-saving notifications regarding incoming missiles and drones, the incident underscores how cyber warfare increasingly targets the psychological wellbeing of civilian populations through disinformation and system sabotage.
According to investigative reports broadcast by BBC News, neither the Kyiv administration nor Moscow has yet verified the origin of the cyber onslaught or pointed fingers at a specific state-sponsored actor. Cybersecurity analysts are currently dissecting the breach to determine whether the attacks originated from a coordinated third-party hacking collective or rival intelligence agencies seeking to escalate tensions.